File Integrity Monitoring: Why It Matters for Modern Cybersecurity
File Integrity Monitoring: Why It Matters
Cybersecurity threats continue to evolve every year, making it more challenging for businesses and individuals to protect sensitive information. While firewalls, antivirus software, and intrusion detection systems play critical roles in security, they are not enough on their own. Attackers often modify important system files, configuration settings, or application data after gaining unauthorized access. Detecting these changes quickly can mean the difference between stopping an attack early and suffering a major security breach.
This is where File Integrity Monitoring (FIM) becomes essential.
File Integrity Monitoring helps organizations detect unauthorized changes to critical files and directories in real time or through scheduled scans. Whether you’re managing a small business website or a large enterprise network, FIM provides valuable visibility into suspicious activity before it causes serious damage.
In this guide, you’ll learn what File Integrity Monitoring is, how it works, why it’s important, its benefits, common use cases, implementation best practices, and the leading tools available today.
What Is File Integrity Monitoring?
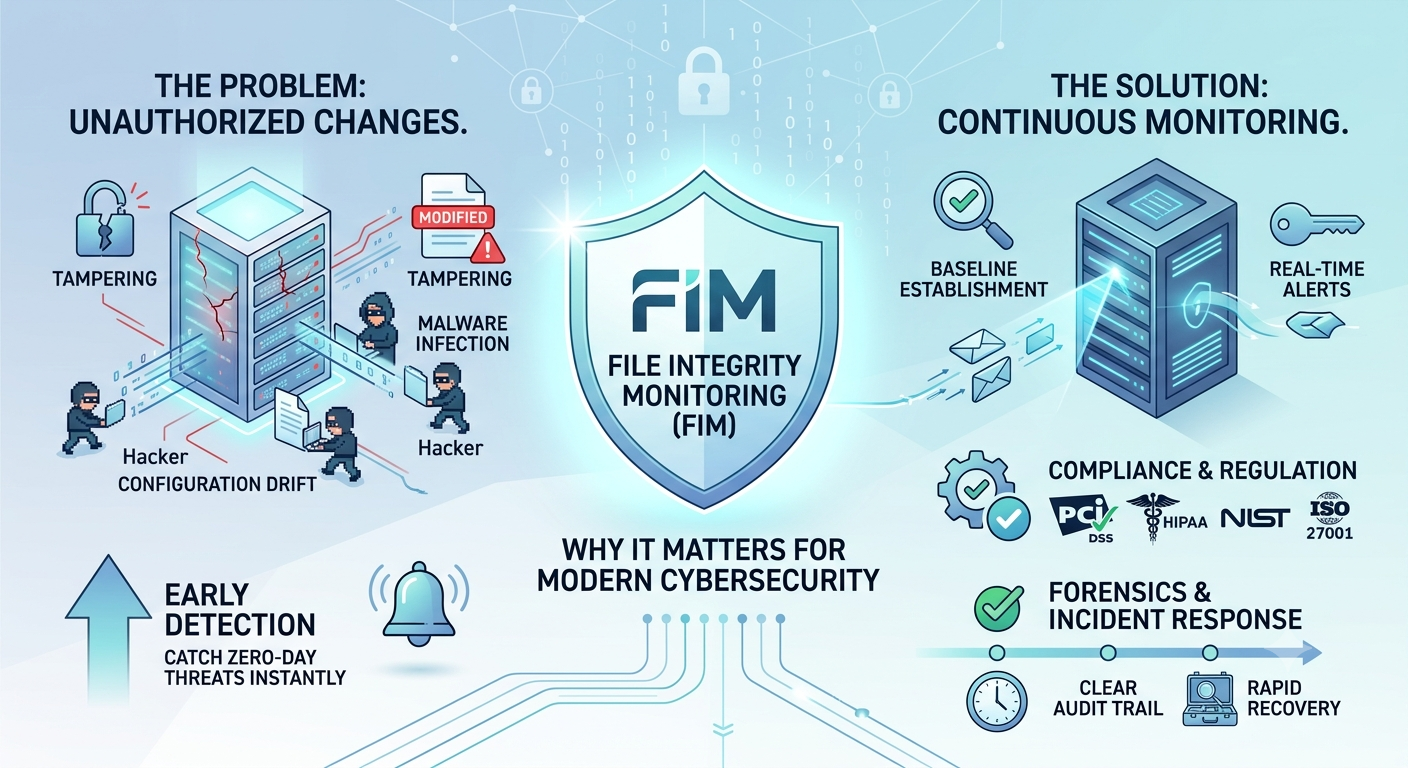
File Integrity Monitoring (FIM) is a cybersecurity process that continuously tracks changes made to important files, operating system components, application files, and configuration settings.
The primary goal is simple:
- Detect unauthorized modifications
- Alert administrators immediately
- Maintain system integrity
- Support compliance requirements
FIM compares the current version of files against a trusted baseline. If unexpected changes occur, administrators receive alerts for further investigation.
Examples of monitored files include:
- System configuration files
- Website files
- Database configuration files
- Security policy files
- User account settings
- Registry entries (Windows)
- Linux configuration files
Why File Integrity Monitoring Matters
Cybercriminals rarely announce their presence. Instead, they quietly modify files to install malware, create backdoors, or disable security controls.
Without monitoring these changes, organizations may remain compromised for weeks or even months.
File Integrity Monitoring helps by:
- Detecting attacks early
- Identifying insider threats
- Preventing unauthorized changes
- Supporting forensic investigations
- Improving compliance readiness
Early detection reduces both financial losses and recovery time.
How File Integrity Monitoring Works
Most File Integrity Monitoring solutions follow a straightforward process.
1. Create a Baseline
The software scans important files and records information such as:
- File name
- File size
- Creation date
- Modification time
- Permissions
- Cryptographic hash values (SHA-256, SHA-512)
This becomes the trusted baseline.
2. Monitor Files
The software continuously or periodically checks monitored files against the baseline.
3. Detect Changes
Whenever a file changes, the software identifies differences such as:
- Modified content
- Permission changes
- Ownership changes
- Deleted files
- Newly created files
4. Generate Alerts
If unauthorized changes occur, administrators receive notifications through:
- Dashboard alerts
- SMS
- SIEM integration
- Security monitoring platforms
5. Investigation
Security teams determine whether the change was:
- Authorized
- Accidental
- Malicious
Appropriate action is then taken.
Types of Changes File Integrity Monitoring Detects
A quality FIM solution can detect many different events.
File Modification
Changes made to existing files.
File Creation
New files added to protected directories.
File Deletion
Removal of important files.
Permission Changes
Unauthorized changes to file permissions.
Ownership Changes
Unexpected changes in file ownership.
Registry Changes
Windows registry modifications that may indicate malware activity.
Configuration Changes
Unauthorized edits to application or operating system configurations.
Benefits of File Integrity Monitoring
1. Faster Threat Detection
The sooner suspicious changes are detected, the faster security teams can respond.
2. Reduced Risk
Attackers often rely on modifying system files. FIM detects these actions before attackers establish persistence.
3. Compliance Support
Many security standards recommend or require File Integrity Monitoring, including:
- PCI DSS
- HIPAA
- ISO 27001
- NIST Cybersecurity Framework
- SOC 2
FIM provides audit logs that help demonstrate compliance.
4. Better Visibility
Administrators gain complete insight into critical file activity across servers and workstations.
5. Incident Investigation
Historical logs make it easier to determine:
- What changed
- When it changed
- Who changed it
- Which systems were affected
6. Protection Against Insider Threats
Not every security incident comes from outside attackers.
Employees with excessive privileges may accidentally or intentionally modify important files.
FIM helps identify these activities quickly.
Common Use Cases
Protecting Web Servers
Website files are common targets for attackers.
Hackers may:
- Inject malicious code
- Replace web pages
- Upload backdoors
- Modify CMS files
FIM quickly detects these changes.
Securing Databases
Database configuration files contain valuable settings.
Unauthorized changes can expose sensitive customer information.
Monitoring Cloud Infrastructure
Cloud servers require the same level of monitoring as on-premise systems.
FIM helps maintain visibility across hybrid environments.
Protecting Financial Systems
Banks and financial institutions rely on FIM to monitor transaction systems and sensitive applications.
Healthcare Security
Hospitals protect patient information by monitoring critical healthcare systems for unauthorized changes.
File Integrity Monitoring vs Antivirus
Many people assume antivirus software provides enough protection.
In reality, the two technologies serve different purposes.
| Feature | File Integrity Monitoring | Antivirus |
|---|---|---|
| Detects file changes | Yes | Limited |
| Detects malware | Limited | Yes |
| Monitors configurations | Yes | No |
| Compliance support | Excellent | Limited |
| Tracks unauthorized modifications | Yes | No |
Using both together provides stronger protection.
Best Practices for File Integrity Monitoring
Identify Critical Files
Focus monitoring on:
- Operating system files
- Website directories
- Configuration files
- Security policies
- Databases
Create Accurate Baselines
Always establish a trusted baseline after verifying the system is clean.
Reduce False Positives
Exclude files that change frequently but are expected to change, such as temporary files and logs.
Enable Real-Time Monitoring
Immediate alerts improve incident response.
Review Alerts Regularly
Ignoring alerts defeats the purpose of monitoring.
Investigate suspicious changes promptly.
Integrate with SIEM
Combining FIM with Security Information and Event Management (SIEM) platforms provides better visibility across the environment.
Keep Software Updated
Regular updates ensure the monitoring solution can detect the latest threats.
Popular File Integrity Monitoring Tools
Several trusted tools are available for organizations of different sizes.
OSSEC
An open-source host-based intrusion detection system with strong file monitoring capabilities.
Wazuh
A popular security platform offering File Integrity Monitoring, vulnerability detection, and log analysis.
Tripwire
One of the oldest and most respected commercial File Integrity Monitoring solutions.
AIDE (Advanced Intrusion Detection Environment)
A lightweight open-source solution commonly used on Linux servers.
SolarWinds Security Event Manager
Provides enterprise-level monitoring and centralized alerting.
Challenges of File Integrity Monitoring
Although extremely useful, FIM has some limitations.
Common challenges include:
- Large numbers of alerts
- Incorrect baseline creation
- Storage requirements for logs
- Resource usage on large environments
- Administrative overhead
Proper planning helps minimize these issues.
Future of File Integrity Monitoring
Cybersecurity continues to evolve rapidly.
Modern FIM solutions increasingly include:
- Artificial intelligence for smarter alerts
- Machine learning for anomaly detection
- Cloud-native monitoring
- Behavioral analytics
- Automated incident response
- Integration with Zero Trust security architectures
These improvements reduce manual work while improving detection accuracy.
Frequently Asked Questions (FAQs)
Is File Integrity Monitoring only for large companies?
No. Small businesses, personal websites, educational institutions, and enterprises can all benefit from monitoring critical files.
Does File Integrity Monitoring stop hackers?
Not directly. FIM detects unauthorized changes, allowing security teams to respond quickly before attackers can cause more damage.
Can File Integrity Monitoring detect ransomware?
Yes. Many ransomware attacks modify or encrypt large numbers of files. FIM can detect these unusual changes and generate alerts.
Is File Integrity Monitoring required for compliance?
Many compliance frameworks, including PCI DSS, recommend or require file integrity monitoring for protecting sensitive systems.
Can Linux and Windows both use File Integrity Monitoring?
Yes. Most modern FIM solutions support Windows, Linux, Unix, and cloud-based operating systems.
Conclusion
File Integrity Monitoring has become an essential component of a modern cybersecurity strategy. As cyber threats grow more sophisticated, organizations need visibility into every critical change occurring within their systems. By continuously monitoring files, detecting unauthorized modifications, and alerting administrators in real time, FIM helps reduce risk, improve incident response, and strengthen overall security.
Whether you manage a personal website, a growing business, or a large enterprise network, implementing File Integrity Monitoring is a proactive step toward protecting valuable digital assets. When combined with strong access controls, regular software updates, endpoint protection, and continuous security monitoring, FIM creates an additional layer of defense that can significantly reduce the impact of cyberattacks.
Investing in File Integrity Monitoring today is not just about meeting compliance requirements—it is about building a stronger, more resilient security posture for the future.